Controls from regulation
Range turns BSA/AML, Travel Rule and MiCA obligations into transaction controls tested against your activity.
Range tests required controls against your real transaction data, then retests as rules and typologies change. Choose a one-off audit or continuous testing between examinations.
$30B+
AUM protected for customers
200+
Networks covered
99.41%
Stablecoin payments tracked
What a Range compliance test delivers
Range turns your requirements into transaction controls, orchestrates your existing screening and compliance providers and tests each control against real data. You get evidence of which controls hold and which fall short.
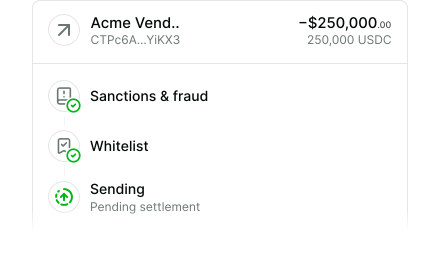
Range turns BSA/AML, Travel Rule and MiCA obligations into transaction controls tested against your activity.
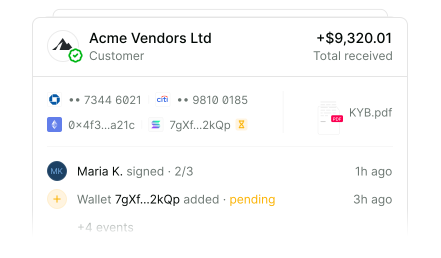
Every control runs against your transaction history and live activity, not samples or self-assessments.
Range compliance experts and engineers embed with your team, bringing blockchain, stablecoin and DeFi experience.
The report maps each control to its obligation and includes evidence for every result. Range supplies the evidence; your team holds the obligation.
One-off audit
Range integrates with your tools, extracts required controls and tests them against your transaction data. Forward-deployed compliance experts and engineers run the assessment and report. Use it before an examination or license application, or after an incident.
Range connects your custodians, wallets, banks, screening providers and networks without replacing your stack.
Required controls run against your transaction data, not a sample.
Compliance experts and engineers embed with your team, run the assessment and deliver evidence for every result.
Continuous testing
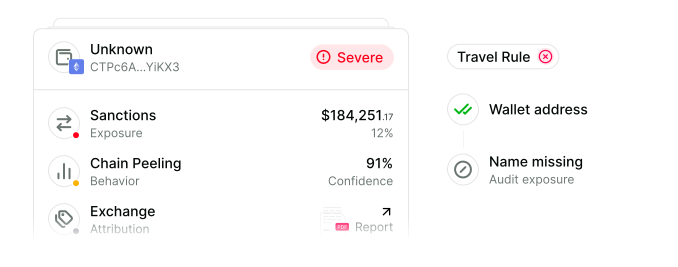
Range continuously tests controls against live data, retests as regulations and typologies change and keeps examiner evidence current. Controls can also run before a transfer is broadcast.
Controls run continuously on live transactions, surfacing failures immediately instead of at the next audit.
When obligations or laundering typologies change, Range updates the controls and retests your history.
Evidence stays current between examinations for auditor, regulator and board review.
How it works
01
Use your existing screening providers, custodians, wallets, banks and supported networks.
02
Range turns your requirements into a testable control set.
03
The forward-deployed team tests each control against your transaction data and records the result.
04
The report maps each control to its obligation and provides a remediation plan for every gap.
Customer workspaces are logically segregated, with strict tenant isolation and internal permission boundaries.
We follow EU data protection requirements for data processing, access, retention and privacy.
Range is undergoing an independent external audit against rigorous security, availability and confidentiality controls.
Layered controls across infrastructure, application, identity and data. Encryption, monitoring, RBAC and least-privilege access at every layer.
More questions on compliance-testing, see the full FAQ.
Book an audit and get a report mapping every control to its obligation.


