Enforce before broadcast
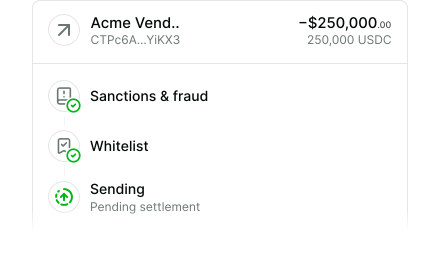
Screen onchain transfers for sanctions, fraud, wrong-address conditions, counterparty risk and payment outliers against the counterparty's established behavior before funds move.
Enforce policy before onchain broadcast, monitor counterparty and treasury risk continuously and have Range prepare the control evidence behind every decision.
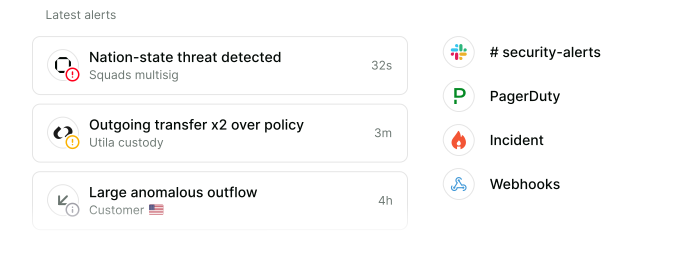
The control gap
Alerts that arrive after an onchain transfer cannot stop it. Range starts with your governing requirements, turns them into operational controls, orchestrates the risk providers already in your stack, then runs monitoring, reconciliation and reporting from the same record.
What Range does for security
Range connects the transaction, counterparty, policy and approval trail. Range workflows run control checks against that record, surface failures and prepare the resulting evidence for security, audit and governance review.
Screen onchain transfers for sanctions, fraud, wrong-address conditions, counterparty risk and payment outliers against the counterparty's established behavior before funds move.
Track asset, custody, chain, protocol and FX exposure continuously across the connected treasury.
Route required signers through multisig approval workflows based on amount, asset, counterparty and policy, then retain the decision reasoning.
Keep screening results, overrides, approvals and alerts in an audit-ready record for review and incident response.
Range products
Protect
Pre-execution sanctions, fraud, operational and counterparty checks.
Protect
Continuous screening on the matched counterparty record.
Protect
Continuous visibility across asset, custody, chain, protocol and FX exposure.
Protect
Detection for exploits, scams, address poisoning and protocol incidents.
Unify
One entity across wallet, exchange and bank identifiers.
Unify
Audit-ready exports for security review, incident response and governance.
Pre-execution security
Range applies the configured policy while the transfer is still pending. The record includes the counterparty, transaction intent, risk signal, approval path and retained decision reasoning.
Check wrong-address conditions and flag payment outliers against the counterparty's established behavior before broadcast. Range does not verify an invoice or expected amount.
Screen for scams, address poisoning, exploit exposure and counterparty risk in the transaction path.
Apply governing controls before broadcast, route multisig approvals and retain the decision reasoning with the transaction.
Keep custody, chain, protocol, asset and FX exposure visible after the transaction is approved.
How it works
01
Connect custodians, self-custody wallets, multisigs, banks and supported networks.
02
Bring approval rules, whitelists, exposure limits and governing requirements into the Range workflow.
03
Screen the onchain transfer, route the required multisig approvals and block broadcast if a configured control fails. Fiat activity raises alerts.
04
A Range workflow gathers the decision trail, applies the configured control tests, flags failures and prepares the evidence pack for security, audit, governance or incident response.
Customer workspaces are logically segregated, with strict tenant isolation and internal permission boundaries.
We follow EU data protection requirements for data processing, access, retention and privacy.
Range is undergoing an independent external audit against rigorous security, availability and confidentiality controls.
Layered controls across infrastructure, application, identity and data. Encryption, monitoring, RBAC and least-privilege access at every layer.
Customer proof

More questions on security, see the full FAQ.
See how Range connects policy, screening, approvals and treasury monitoring in one control layer.


