Unify the book
View reserves, operating positions and counterparty exposures across custodians, wallets and bank accounts in one normalized ledger.
Give digital-asset operations one ledger, transaction-level controls and reporting workflows that prepare examiner-ready evidence without replacing custody or compliance infrastructure.

The operating gap
A bank can add custodians, wallets and stablecoin rails without gaining one defensible record above them. Start with the requirements examiners and internal policy set. Range turns those requirements into operational controls, orchestrates existing risk and compliance providers, then runs monitoring, reconciliation and reporting from the same ledger.
What Range does for banks
Range sits above custodians, wallets, correspondent accounts and existing compliance providers. Range workflows use the shared transaction and counterparty record to gather evidence, apply bank policy, resolve exceptions and prepare the reporting result for review.
View reserves, operating positions and counterparty exposures across custodians, wallets and bank accounts in one normalized ledger.
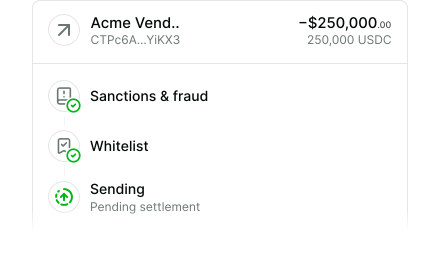
Screen onchain transactions before broadcast and route approvals by amount, asset, counterparty and policy. Fiat activity raises alerts.
Match cross-rail movements, classify activity and keep the underlying source record available for review.
Retain screening, approval and counterparty history for examiner, auditor, board and correspondent review.
Range products
Unify
Real-time positions across custodians, wallets, correspondent accounts and operating banks.
Protect
Pre-execution controls for onchain transfers, with alerts on fiat activity.
Unify
One entity across wallet, exchange and bank identifiers.
Unify
Normalized and classified activity across fiat and stablecoin rails.
Protect
Continuous visibility across asset, custody, chain, protocol and FX exposure.
Unify
Examiner, auditor, board and correspondent reporting from the same ledger.
How it works
01
Connect custodians, self-custody wallets, multisigs, bank accounts, supported networks and existing compliance providers.
02
Bring internal treasury policies, approval rules, counterparty requirements and exposure limits into Range.
03
Screen onchain transfers before broadcast, raise alerts on fiat activity and route approvals through the correct signers.
04
A Range workflow assembles transaction decisions, counterparty histories, positions and control evidence, surfaces exceptions and prepares the review-ready result.
Customer workspaces are logically segregated, with strict tenant isolation and internal permission boundaries.
We follow EU data protection requirements for data processing, access, retention and privacy.
Range is undergoing an independent external audit against rigorous security, availability and confidentiality controls.
Layered controls across infrastructure, application, identity and data. Encryption, monitoring, RBAC and least-privilege access at every layer.
Regulatory posture
Range supplies controls, audit trails, evidence and reporting that support a bank's regulatory program. Range routes Travel Rule data across integrated VASP network providers. The bank remains responsible for determining and meeting its obligations in every jurisdiction.
Regulated transfers require accurate originator and beneficiary data, with obligations varying by market and corridor. Range routes Travel Rule data across integrated VASP network providers and keeps coverage and completeness evidence with each transfer.
Transaction-monitoring programs must cover the expected activity and escalate alerts on time. Range reconciles expected and monitored transactions, then retains coverage, configuration and escalation evidence for review.
Banks must screen relevant counterparties and activity against the applicable sanctions lists and document the resulting action. Range records each screening result, the list version used and the decision trail for review.
Banks must maintain reconciled records and produce the reserve, safeguarding, custody and transaction reports required in each market. Range keeps the source activity, reconciliations and governed reporting inputs together in one review-ready record.
Operating model
Range sits above custody, banking, wallet and compliance systems, linking each transaction to its counterparty, policy, approval and reporting evidence. Finance, compliance and risk teams work from the same record while existing providers stay in place.
Story 1 of 2
Related reading

More questions on banks, see the full FAQ.
Review how one ledger can support transaction controls, reconciliation and examiner evidence across digital assets and fiat.


